Most people tap “Allow” on every permission request and scroll past every privacy policy without reading a word. That habit was already risky before AI apps existed — now it’s worse, because a growing number of apps use “AI” as the headline feature while the real business model underneath is harvesting conversations, photos, and behavior data to sell to advertisers or data brokers. Here’s how to actually tell the difference, and the specific checks that take less time than you’d think.
Step 1: Check whether the privacy policy even names the app
This is the fastest, most telling check on this entire list, and almost nobody does it. Open the app’s privacy policy and search for the app’s actual name. A legitimate company writes a policy specific to its product. A red flag operation often pastes in a generic, boilerplate policy — sometimes one that still references a completely different product name, a leftover from a template they never bothered to customize. If you can’t find the app’s own name anywhere in its privacy policy, that’s not a minor oversight; it’s a sign nobody is actually accountable for what that document says.
Step 2: Search the policy for three specific words — not the whole document
You don’t need to read every page. Use your browser’s find-in-page function (Ctrl+F or Cmd+F) and search for “train,” “third party,” and “share.” These three words surface the paragraphs that actually matter — whether your conversations are used to train AI models, who else receives your data, and under what circumstances it’s shared or sold. A policy that’s vague here, full of hedging language like “may” and “might” rather than clear, direct statements, is a genuine red flag on its own — real commitments are specific; evasive language usually means the company wants room to do more with your data than it’s willing to say plainly.
Step 3: Check whether requested permissions actually match what the app does
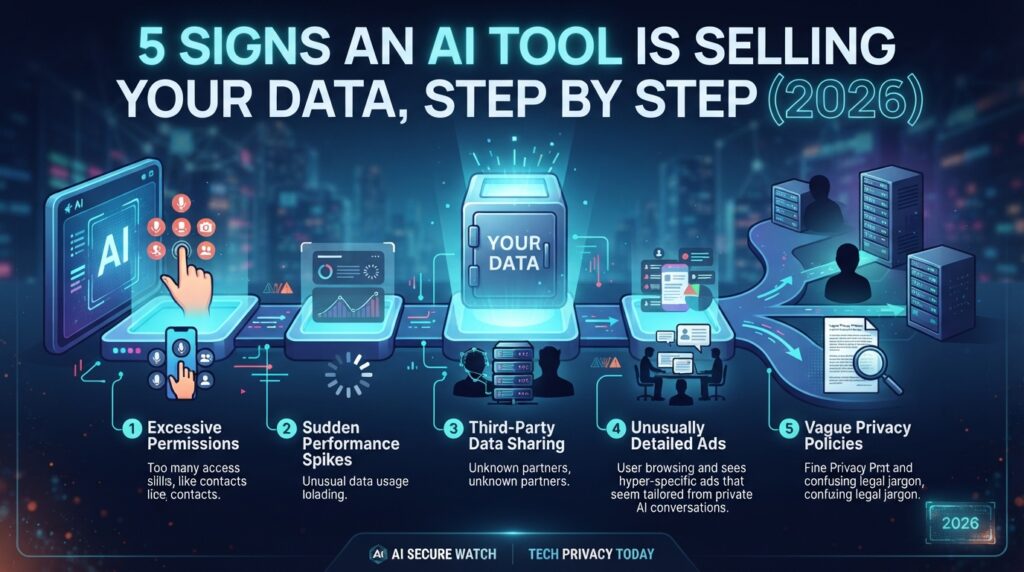
Open your device settings — iOS: Settings → [app name] → Permissions; Android: Settings → Apps → [app name] → Permissions — and look at what the app can access: microphone, camera, contacts, location, photos. Then ask a simple question for each one: does this app genuinely need this to do what I use it for? A voice-based AI assistant has an honest reason to want your microphone. A text-based chatbot asking for your contacts and precise location does not. Mismatched permissions are one of the most consistently cited red flags across security research — excessive access isn’t accidental, it’s a business decision.
Step 4: Find out whether you can actually delete your data — and try it
Look for an account deletion or data export option, typically in account or privacy settings. Then actually test it if you’re able to. A trustworthy app makes this straightforward. If you can’t find any way to delete your data, or deletion only removes your account login while vaguely implying your actual content is “retained for other purposes,” that’s a serious problem — your data should be yours to remove, not something the company quietly keeps regardless of what you asked for.
Step 5: Check whether data-sharing settings default to on or off
This is the most overlooked check on the list, and one of the most important. Open the app’s data or privacy settings and look for any toggle related to personalized advertising, data sharing with partners, or using your conversations to train models. The question that matters isn’t just whether an opt-out exists — it’s what the default setting already is before you touch anything. A genuinely privacy-respecting app defaults these settings to off, requiring you to actively opt in. An app that quietly defaults to on, hoping you never go looking, is using your inattention as part of its business model.
What to do if an app fails these checks
You don’t need to delete every app that has one weak answer — but an app that fails two or more of these five checks is worth replacing, especially if it handles anything sensitive (health information, financial details, private conversations). Set a recurring reminder to redo this full check quarterly, since privacy policies and default settings both change over time, often quietly, without any real notice to existing users.
Frequently asked questions
It’s common, but it should always be disclosed clearly and, ideally, something you can opt out of. The difference between a trustworthy app and a risky one isn’t whether training happens at all — it’s whether the app tells you plainly and gives you real control over it.
Not always, but it’s a reasonable thing to check more carefully. Many free apps genuinely are ad-supported without harvesting conversation content, while others monetize through data sales specifically because there’s no other revenue model. The five checks above tell you which situation you’re actually in, rather than guessing from the price alone.
Step 3 — check your device’s permission settings for that app. It takes under a minute and immediately reveals whether the app is asking for more access than its actual function requires.
Yes, somewhat — these apps often collect emotionally sensitive conversation content, and research has found some bury their privacy policies in hard-to-find places specifically to discourage this kind of review. Apply all five checks, not just a quick skim, before trusting one with anything personal.
Yes — a recipe app or photo editor that’s added an AI feature deserves the same scrutiny as a dedicated AI app. Check whether the new AI feature introduced new permission requests or new data-sharing language in an updated privacy policy; features get added quietly far more often than entire new apps do.
Compiled and cross-referenced across multiple 2026 digital privacy and AI safety trackers, including guidance consistent with GDPR’s data protection standards. One note on regulatory context: the EU AI Act’s transparency obligations (requiring disclosure when you’re interacting with AI) took effect August 2026, but its broader high-risk system protections were pushed back by a mid-2026 regulatory change (the “Digital Omnibus”) to December 2027 and August 2028 depending on category — meaning the legal backstop in the EU is less complete right now than many summaries suggest, which makes checking these five signs yourself more important, not less. This is general safety guidance, not legal advice — for apps handling particularly sensitive data, consider consulting your jurisdiction’s specific data protection resources.